
Compliance Should Start With Infrastructure
For iGaming operators, compliance is often associated with audits, documentation, policies and regulatory approvals. But many of the controls required to support MGA compliance, PCI DSS and ISO 27001 are ultimately connected to something more fundamental: the underlying technology environment.
- How is access managed?
- Where is sensitive data stored?
- How are systems monitored?
- Can infrastructure changes be tracked?
- What happens when traffic suddenly increases?
- How quickly can an operator respond to a security incident?
These are not questions that should only be answered before an audit.
A stronger approach is compliance by design – building security, governance and operational controls directly into the iGaming cloud infrastructure from the beginning.
This approach can make compliance easier to manage while also creating a more secure and scalable foundation for growth.
What Does Compliance by Design Mean for iGaming?
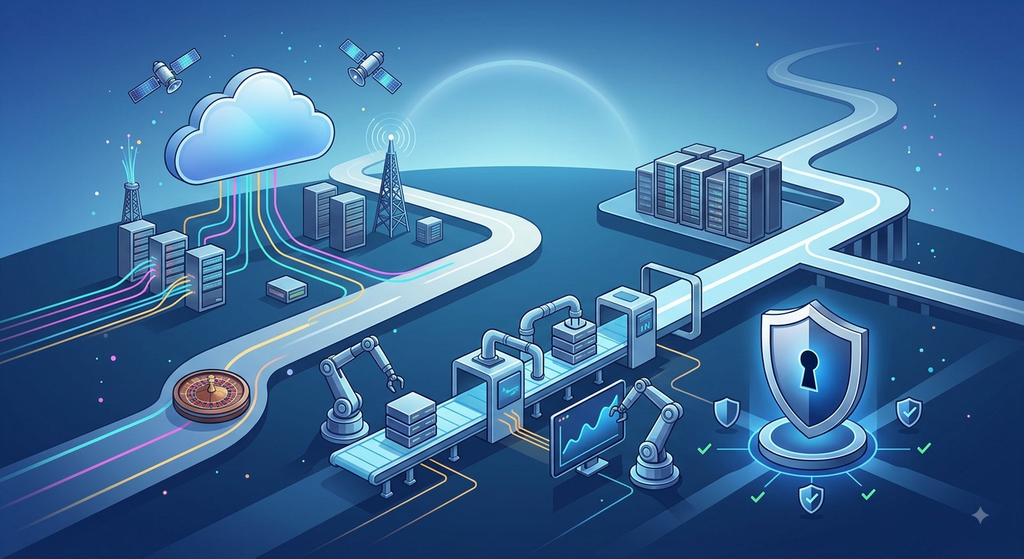
Compliance by design means that regulatory and security requirements are considered during the architecture and infrastructure planning stages rather than being added later.
For an iGaming company, this could include designing the cloud environment around principles such as:
- Least-privilege access
- Network segmentation
- Encryption and secure key management
- Centralized logging and monitoring
- Infrastructure change tracking
- Backup and disaster recovery
- Secure deployment processes
- Continuous security controls
- Clear ownership of systems and data
Instead of treating compliance as a separate project, these controls become part of everyday infrastructure operations.
This is particularly valuable for operators working across multiple markets, where regulatory requirements can vary and evolve over time.
MGA Compliance: Building Infrastructure Around Governance
The Malta Gaming Authority (MGA) operates within a highly regulated iGaming environment, making governance and security important considerations for operators.
While regulatory compliance extends beyond technology, infrastructure plays an important supporting role.
A well-designed environment should provide visibility into:
- Who can access production systems
- What resources are running
- Where sensitive information is stored
- What changes have been made
- How security events are detected
- How incidents can be investigated
Cloud governance can help establish these controls consistently.
For example, a properly structured AWS or Azure Landing Zone can establish baseline account structures, identity controls, networking, security policies and logging before applications are deployed.
This creates a repeatable foundation rather than configuring security differently for every environment.
PCI DSS: Protecting the Payment Environment
PCI DSS compliance is particularly relevant to iGaming because operators frequently handle payment-related information and integrate with multiple payment service providers.
One of the biggest challenges is understanding and controlling the PCI DSS scope of the environment.
A secure cloud architecture can help separate sensitive workloads from other components of the platform through:
- Network segmentation
- Restricted access
- Strong identity and authentication controls
- Encryption
- Centralized monitoring
- Secure configuration management
- Controlled deployment processes
The objective isn’t simply to “pass PCI DSS.”
The goal is to create an environment where the security controls supporting PCI DSS are part of normal operations.
This can also make future infrastructure changes easier to assess because security boundaries and responsibilities are clearly defined.
ISO 27001: Turning Security Into an Operating Model
While PCI DSS focuses heavily on payment card data and security controls, ISO 27001 takes a broader approach to information security management.
For iGaming companies, this means technology needs to work alongside processes, policies, risk management and governance.
From an infrastructure perspective, this can involve:
- Identity and access management
- Asset management
- Security monitoring
- Vulnerability management
- Incident response
- Business continuity
- Backup strategies
- Configuration management
The important point is that ISO 27001 should not be treated as a document-generation exercise.
Infrastructure needs to support the security management processes that the organization has established.
DevSecOps: Bringing Compliance Into the Deployment Pipeline
One of the challenges with traditional compliance models is that infrastructure can change much faster than compliance documentation.
An iGaming platform may deploy new application versions, infrastructure components or cloud resources frequently. Manually checking every change is difficult to scale.
This is where DevSecOps can help.
Security and compliance checks can be incorporated into CI/CD pipelines so that infrastructure and application changes are evaluated before reaching production.
For example, automated controls can check for:
- Misconfigured cloud resources
- Excessive permissions
- Vulnerable dependencies
- Security policy violations
- Infrastructure configuration issues
This creates a more continuous approach to compliance instead of relying entirely on periodic reviews.
For companies building this type of environment, platforms such as ITGix DevSecOps can provide a foundation for integrating security into the software delivery lifecycle.
Building a Cloud Foundation That Can Scale
Compliance is only one part of iGaming infrastructure.
The environment also needs to support unpredictable traffic, new markets, integrations and rapid product development.
This is why cloud architecture should consider security, scalability and governance together.
A structured cloud foundation can provide standardized networking, identity, security controls, logging and account management before individual workloads are introduced.
For example, a Landing Zone approach can help establish a repeatable cloud architecture for different environments and workloads. ITGix’s AWS Landing Zone and Azure Landing Zone services are examples of how this type of foundation can be implemented without making every new environment a completely separate infrastructure project.
The benefit is not simply technical consistency. It can also make security and governance easier to maintain as the platform grows.
A Practical Example: From New Platform to Production
Consider an iGaming operator preparing to launch a new platform.
Instead of deploying the application first and addressing compliance requirements afterward, the company establishes its cloud foundation upfront.
The environment includes:
- Separate production and non-production environments.
- Centralized identity and access management.
- Network segmentation for sensitive workloads.
- Centralized logging and monitoring.
- Encryption and secure key management.
- Automated infrastructure security checks.
- Backup and disaster recovery processes.
- Controlled CI/CD pipelines.
The result is an infrastructure environment where security and governance are built into the architecture rather than manually added after deployment.
With the right cloud foundation and automation, production environments can also be prepared significantly faster – in some cases, in under a week – while maintaining the controls needed for security and governance.
How iGaming Compliance Supports Faster Market Expansion
One of the biggest advantages of this approach appears when an iGaming operator expands into another market.
Starting from scratch for every new jurisdiction can create unnecessary infrastructure work.
A standardized cloud foundation allows organizations to reuse established patterns while adapting specific components to local regulatory requirements.
This is particularly important as operators navigate different combinations of MGA requirements, PCI DSS, ISO 27001, local regulations and security expectations.
The architecture does not need to be regulator-specific.
It needs to be flexible enough to accommodate regulatory change.
Build Infrastructure That Is Ready for Compliance
For modern iGaming companies, compliance should not be something that happens immediately before an audit or market launch.
MGA compliance, PCI DSS and ISO 27001 all benefit from a strong underlying foundation of security, governance and operational control.
By adopting compliance by design, iGaming operators can build cloud infrastructure that is:
- More secure
- Easier to govern
- Easier to monitor
- Better prepared for audits
- More adaptable to regulatory changes
- Ready to support future market expansion
The goal is not simply to build infrastructure that meets today’s requirements.
It is to build an environment that can adapt as the business, technology and regulatory landscape evolve.
Build a More Compliance-Ready iGaming Cloud Environment
Whether you’re preparing for a new market launch, reviewing your existing cloud architecture or strengthening your security and compliance posture, the right infrastructure foundation can make the process significantly more manageable.
ITGix helps iGaming organizations design secure, scalable and governance-ready cloud environments, combining cloud architecture, Landing Zones and DevSecOps practices to support compliance and faster market entry.
Want to assess whether your current iGaming infrastructure is ready for the next stage of growth? Book a free consultation with ITGix.

